

Hotel Wi-Fi and account security are connected, but the network is only one part of the picture. A legitimate connection cannot protect you from entering a password on a convincing fake website. Equally, using a shared network does not mean every message or banking session is automatically visible to other guests.
A useful travel routine combines a verified connection, current devices, strong sign-in protection, and a moment of attention before you respond to unexpected requests. Prepare those basics before departure, then make a few deliberate choices when you connect at the hotel.
Understand what an encrypted connection protects
The Federal Trade Commission’s public Wi-Fi guidance explains that widespread website encryption has made using public Wi-Fi generally safer than it was in the early internet era. HTTPS protects information traveling between your browser and the website. It is a meaningful protection, including on shared networks.
However, encryption does not establish that the website belongs to an honest organization. A fraudulent page can also use HTTPS. Check the address and the reason for the request, especially before entering payment details, passwords, or identity information. A browser security indicator is not a recommendation of the business behind the page.
Do not dismiss a browser warning about an invalid or untrusted connection simply because you need to get online quickly. Pause and ask the hotel for help with its connection process. If something remains unclear, use another connection you trust or wait before handling sensitive tasks.
Confirm the hotel’s connection process
Ask reception for the exact network name and how guests sign in. A familiar-looking hotel name in the network list is not enough to verify who operates it. Clarify whether access is included and whether a room number, access code, or separate account is needed.
If the sign-in page asks for unexpected information, check before proceeding. A hotel access code and your email account password serve different purposes. Do not give someone your account password to troubleshoot Wi-Fi or approve an unrelated sign-in request because a person claims to be technical support.
Prepare devices and accounts before traveling
Install operating-system, browser, and app updates through their normal settings or official stores. The FTC’s personal-information protection guidance recommends keeping security protections current. Avoid treating an unexpected pop-up on a hotel sign-in page as a trusted software update.
Set a screen lock and know how to recover important accounts if your phone becomes unavailable. Save essential travel details where you can reach them without depending on a single app session. For work devices, check your organization’s travel and remote-access requirements before leaving.
Use a different strong password for each account
The FTC’s account-protection guidance recommends strong passwords and explains how a password manager can help. Prioritize the email account that receives password-reset messages, along with financial and booking accounts. Reusing a hotel membership password for your main email creates unnecessary dependence between accounts.
Make recovery possible away from home
Review recovery email addresses and phone numbers before the trip. If an account offers backup codes, store them securely where you can retrieve them without relying solely on the device they are meant to replace. Do not paste codes into shared booking notes or send them to someone offering unsolicited help.
Add protection beyond a password
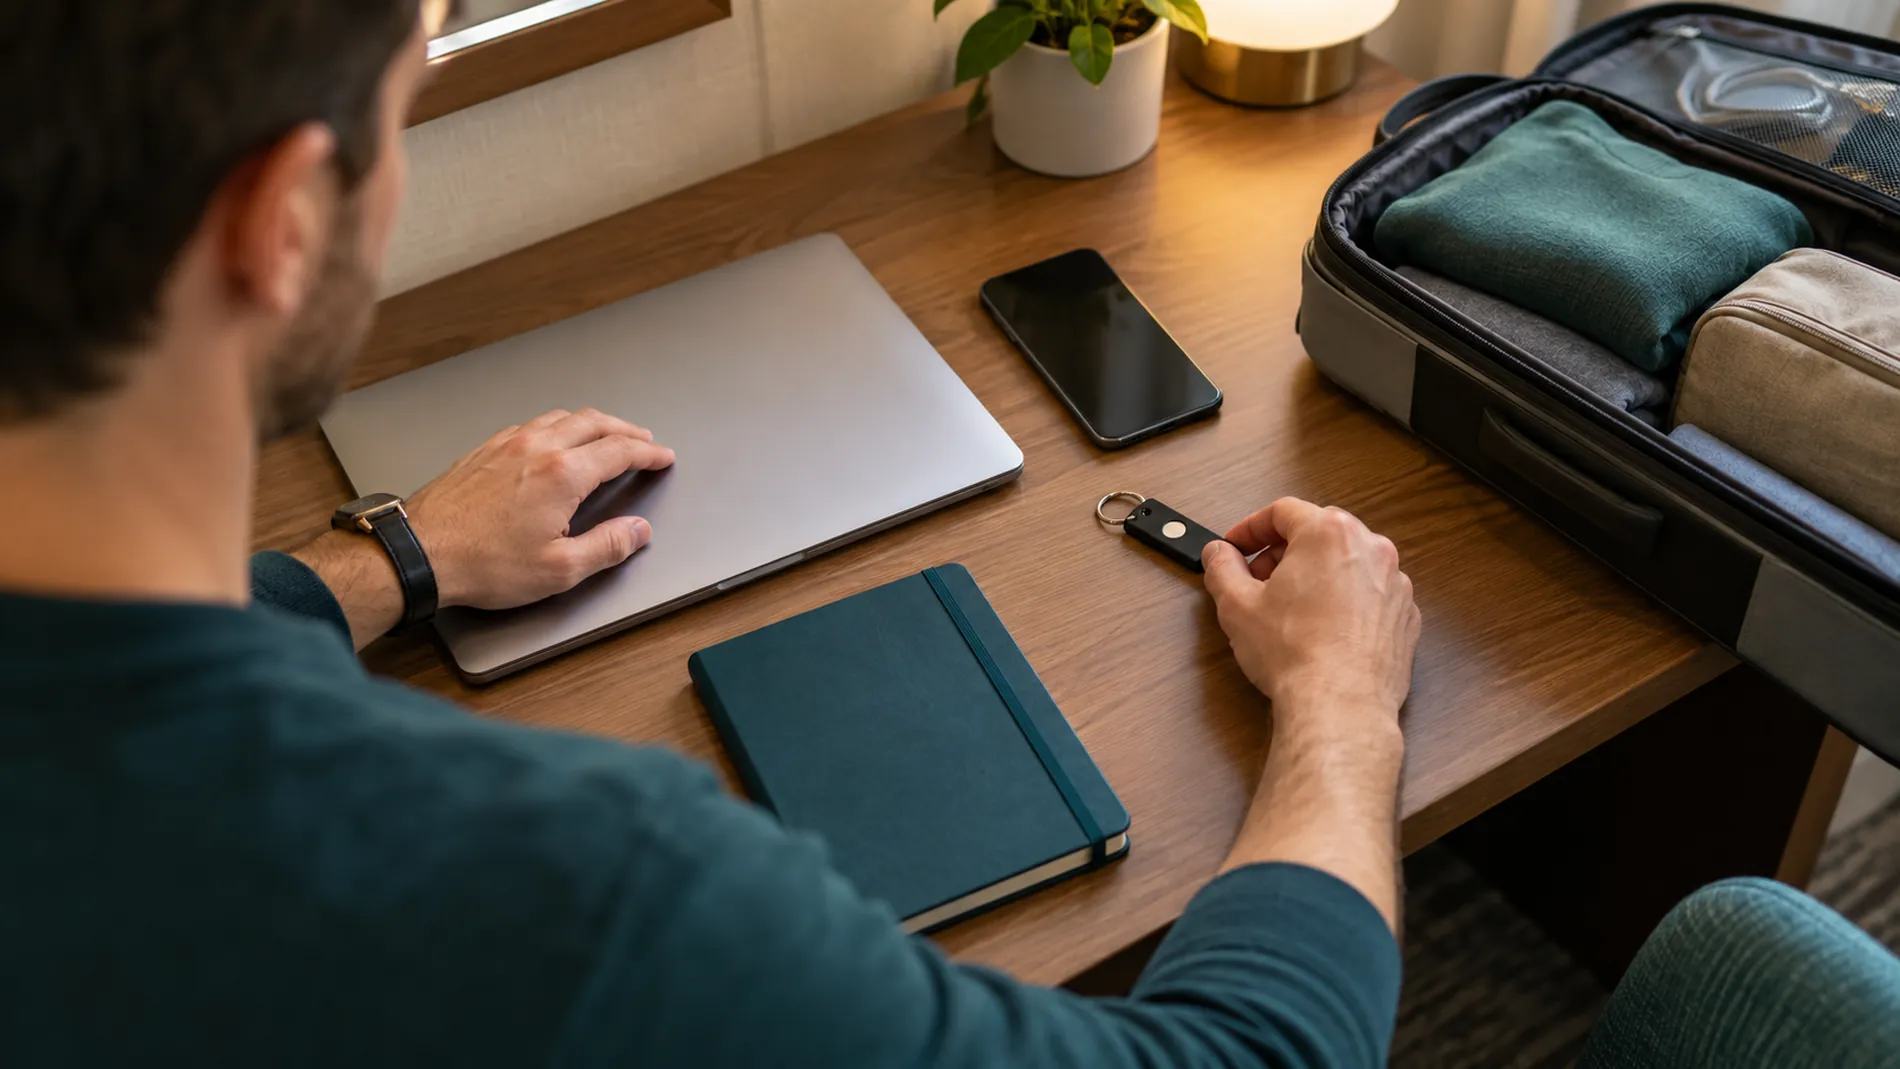
Turn on two-factor authentication where available. The FTC describes options such as authentication apps and security keys. Test your chosen method before traveling, especially if your phone number may not receive messages abroad. Keep access practical as well as protected.
Consider a passkey when a service supports it. Passkeys use sign-in technology that can tie authentication to the genuine site’s domain, helping resist lookalike login pages. NIST’s digital identity guidance explains this phishing-resistant property of WebAuthn authenticators. Account recovery and device protection still matter; no sign-in method makes every scam harmless.
Only approve authentication prompts for a sign-in you are actually making. An unexpected request is a reason to investigate through the service’s normal app or website, rather than repeatedly approving prompts to make them disappear.
Watch for messages that borrow your travel context
A message about a failed deposit or urgent booking verification can seem plausible during a trip. The FTC’s phishing guidance recommends checking unexpected requests through contact information you independently know is genuine. Open your existing booking app or call the property’s verified number rather than following the message’s link.
Verify the request before responding
Be especially careful when the message creates pressure to pay immediately, reveal a login code, or download a file. Our guide to hotel booking scams covers payment requests in more detail. Knowing your stay dates does not, by itself, prove that a sender is authorized to collect money.
Choose a working setup you can manage
Use your own device for sensitive accounts when practical. In shared lounges, position the screen so casual passersby cannot easily read private information, and lock it when you step away. Keep devices under your control using the routine in our guide to keeping track of hotel valuables.
If your employer requires a VPN, use the approved service and follow its instructions. Do not assume that a VPN can correct a fraudulent website or a password you willingly disclose. For a questionable connection, mobile data may be a convenient alternative, subject to your plan and coverage.
At the end of a working session, check what you have left open. Close sensitive documents, lock the device, and collect any printed pages before leaving a shared space. If you used a hotel television or another shared device for an account, sign out through that service and check its device-management settings when appropriate.
Keep help requests specific. Tell reception that the expected network is missing, the access code fails, or the sign-in page looks different from the instructions. You can explain those problems without handing over an unlocked phone containing private messages or exposing a password to someone standing beside the desk.
Respond promptly if you disclose account information
If you entered credentials on a suspicious page, stop using that page and open the service through its trusted app or known address. Change the affected password and any reused versions, review recovery settings and signed-in devices, and follow the provider’s account-recovery instructions. Contact your employer promptly if work information is involved.
For payment exposure, contact the issuer through its official channel. Save relevant messages and a factual timeline without publicly posting private credentials. Our guide to recording a hotel incident can help organize that follow-up. Keep the response focused on the information actually disclosed and the accounts that need protection.